Certified AI Security Officer
You already run the security function. What you have not been tested on is the boardroom — defending a budget to a CFO who wants a number, translating risk into language a CEO will act on, and owning the decision when a ransomware attacker gives you an hour to answer. CAISO runs that tenure end to end, against one continuous executive cast, then puts you through two live crisis simulations where the wrong call has a five-year cost.
30 Nov to 5 Dec 2026
- 5 evenings
- Mon 30 Nov to Fri 4 Dec, 18:00 to 20:00 IST, live online
- Immersion day
- Sat 5 Dec, 11:00 to 16:00 IST, live boardroom simulations
Online, international coverage
Full schedule ↓Curriculum reviewed by 13 independent security and governance leaders from the CSA Bangalore network.
9 modules · 6 sessions
Six leadership frameworks plus three live crisis simulations, across 5 evenings + a Saturday immersion
$20M
Ransomware boardroom simulation — five roles, five stages, one deadline
Practitioner-level
Certification, human-graded not auto-scored
Leader-built
For team leads, security managers and aspiring CISOs — not implementers
Built on the frameworks
Discounted price ₹33,500 (this cohort only). List price ₹61,500. Five live 2-hour evening sessions plus a full-day Saturday immersion, taught virtually with international coverage. Includes all assignments, labs and the certification assessment.
A CISO was criminally convicted in 2022 for how a breach was handled, not for the breach itself. Most security leaders have never rehearsed that boardroom. Next cohort starts 30 Nov 2026.
Register for the CohortSee the CAIGL ProgrammeCorporate & group discounts — Contact us“This was a different learning experience altogether… I recommend this learning methodology to every learner.”
— Pravinkumar Jha, Head of Product and Cloud Security
This course includes
- Five live 2-hour evening sessions plus a full-day Saturday immersion
- Run online with international coverage — join from any timezone
- All 9 modules taught live across 5 evening sessions and the Saturday immersion: six leadership frameworks plus three live crisis simulations
- Assignments and hands-on labs between sessions, reviewed by the faculty
- 40 MCQs + 8 written responses, human-reviewed
- AI implications built into every module
- Joins from any device — sessions are recorded for the cohort
Why This Course
You already run a security function. CAISO is where you rehearse the part of the job nobody trains you for: defending a budget to a CFO who tests every number, translating a technical risk into a decision a CEO will actually make, and knowing exactly where personal liability lands when a regulator calls. One continuous scenario runs across all nine modules — the same CFO, CEO, General Counsel and mentor CISO recur and escalate, so a boardroom skill you build in Module 4 is the one you are tested on again in the live crisis simulations.
Built around: SABSA · STRIDE & PASTA · FAIR · NIST CSF · ISO/IEC 27001 · EU AI Act
Skills You’ll Gain
Who Should Attend
Team Leads
Technical or operational leads ready to take on programme-level ownership and board-facing responsibility for the first time.
Security Managers
Managers running a security function day to day who need the architecture, budget, and communication frameworks a CISO role demands.
Aspiring CISOs
Anyone deliberately building toward a CISO or Head of Security title, including from an adjacent function like IT or risk.
What this role is hired for, and what it pays
No verified job posting carries the exact title "CAISO" — this course maps to the CISO and senior security-leadership hiring track itself, the role its curriculum targets. The two examples below are stable careers pages, not single postings that will 404; verify current openings directly on each employer’s site.
Chief Information Security Officer — Tata Consultancy Services
One of India’s largest recurring employers of CISO and security-leadership roles, spanning enterprise security architecture, risk and regulatory engagement across client accounts.
Chief Information Security Officer — Standard Chartered
Security-leadership hiring inside a regulated financial institution, where CISO personal liability and board-facing risk reporting are a live part of the role.
What CISOs earn in India
Third-party compensation trackers report the average CISO salary in India around ₹42.6L, ranging from roughly ₹30L at entry level to ₹55L+ at senior level, with Bengaluru running higher than the national average (~₹50L) and CISOs specialised in AI/LLM security reported at ₹85L–1.2Cr+. These are third-party estimates, not a CyBe Global placement guarantee — check a primary board (Glassdoor, PayScale, AmbitionBox) for your own experience level and city before treating any figure as fixed.
Company names and logos are used only to identify where these roles were publicly posted at the time of writing, and do not imply that TCS or Standard Chartered endorse, sponsor or are affiliated with CyBe Global or this programme. Salary figures are third-party market estimates, not a placement or compensation guarantee.
Curriculum
6 sessions · 33 lessons
Evening 1
Mon 30 Nov, 18:00–20:00 IST
Enterprise Security Architecture + Enterprise Threat Modelling
SABSA’s six layers from business context down to operations, then STRIDE and PASTA at enterprise scale — Diane sets the tenure’s framing on day one
You learn SABSA’s six architectural layers and how each answers a different business question, plus the core principles — defence in depth, least privilege, security as an enabler rather than a list of prohibitions — and where AI changes the architecture. Diane opens the tenure here: work back from the business, not the tools. Then you apply STRIDE across all six threat categories at enterprise scale, and run PASTA’s seven stages to build a risk-centric model focused on adversary goals rather than component checklists — including AI as both a new threat actor and a new threat-modelling tool.
Skill: Think in architectures, not just controls, and threat-model at the scale a real enterprise actually presents
Evening 2
Tue 1 Dec, 18:00–20:00 IST
Building and Managing a Security Programme + Board Communication
Maturity models and the 90-day CISO roadmap, then the one-page board brief — Sandra’s counsel and the board scene where Marcus and Priya both weigh in
You learn to baseline a programme against CMMI, NIST CSF Tiers and C2M2, choose the right model for board reporting versus internal management, and build a 90-day roadmap that shows quick wins while laying real foundation. Sandra’s counsel lands here: don’t announce changes before you understand the org. Then you learn to translate technical risk into business language, structure a one-page four-quadrant board brief, and pick 3-4 metrics a board will actually act on — tested live in the board scene, where Marcus challenges the numbers and Priya watches the liability.
Skill: Build a programme that survives contact with a board, and defend it in the room
Evening 3
Wed 2 Dec, 18:00–20:00 IST
Security Budget, ROI, Vendor Management + Metrics, Regulatory Engagement
The FAIR model against Marcus’s ROI pushback, then KPIs, KRIs and the personal-liability peak with Priya, Sandra, and the regulator
You learn to quantify risk in financial terms with the FAIR model — Annual Loss Expectancy, the case for investment — against Marcus’s set-piece skepticism ("we have never had a ransomware attack, so the frequency is zero"), then structure a Run/Change/Leap budget and score vendor RFPs against a fixed framework, including AI vendor due diligence. You then design a KPI/KRI programme using the five-element metric standard, and reach the tenure’s liability peak: engaging regulators without converting a civil matter into a criminal one, and understanding personal CISO liability after the 2022 Uber conviction — with Sandra’s "I have sat where you are sitting, in front of the SEC."
Skill: Make the financial case a CFO cannot wave away, and know exactly where liability lands before you need to
Evening 4
Thu 3 Dec, 18:00–20:00 IST
The Ransomware Boardroom Game
A live 5-role, 5-stage boardroom simulation of a $20M ransomware attack
The tenure turns live: TechNovaCloud has been hit by a $20M ransomware attack, and you play CEO, CIO, CISO, Head of Legal, or an external consultant through five stages — identification, containment, analysis and the pay-or-not-pay decision, eradication, and recovery — under a hard deadline and real OFAC-sanctions stakes.
Skill: Lead a live incident response in role, under real time pressure, and defend the pay-or-not-pay call
Evening 5
Fri 4 Dec, 18:00–20:00 IST
The Shadow AI Reckoning
A discovery audit becomes an AI Tool Register and a 5-pillar Acceptable Use Policy, mapped to the EU AI Act and GDPR Article 22
You run a shadow AI discovery audit using proxy logs, expense reports and department interviews, convert the findings into an AI Tool Register, and draft a 5-pillar Acceptable Use Policy — resisting the ban instinct, since a blanket ban only manufactures ungoverned shadow IT. You map the estate to the EU AI Act risk classes and GDPR Article 22.
Skill: Answer a regulator who asks what AI you actually run, with a register and a policy instead of a ban
Immersion Day
Sat 5 Dec, 11:00–16:00 IST
The Poisoned Matrix: AI Security War Room + Certification
CAPSTONEA five-stage adversarial AI incident at NimbusMind, run from five executive seats, then the certification assessment: 40 MCQs plus 8 written responses, human-graded
The tenure closes with its highest-stakes scenario: an adversarial AI compromise at NimbusMind, run live from five executive seats through identification, containment, the pay-or-resist decision, eradication, and post-incident governance reform. You sequence the first hour so containment does not destroy the forensic evidence eradication depends on, weigh pay-or-resist against sanctions exposure and an unverifiable deletion guarantee, and trace the incident to its root cause in the AI supply chain rather than patching posture generally. The day closes with the certification assessment: 40 scenario-based multiple-choice questions plus 8 written leadership responses — board memos, budget cases, incident summaries — graded by a senior practitioner, not auto-scored.
Skill: Run an AI security incident end to end under fire, then prove the judgment behind it under assessment
Upcoming cohort dates
The same leadership content delivered as a facilitated CAISO cohort, run in executive cabinets of four with two live boardroom crisis simulations. Inaugural early-bird price: ₹33,500 per seat (this cohort only), down from the list price of ₹61,500. One cohort, run with international coverage at the request of our global members: five 2-hour evening sessions Monday to Friday, then a full-day Saturday immersion.
November–December 2026 cohort
Online — international coverage
5 sessions · 18:00–20:00 IST
- Mon 30 Nov
- Tue 1 Dec
- Wed 2 Dec
- Thu 3 Dec
- Fri 4 Dec
Cabinets are capped at 24 participants per cohort, because the live boardroom simulations depend on that structure. Private cohorts for a single leadership team run on a date of your choosing.
What backs this up
The specifics behind the claims on this page. Open any of them for the detail.
Scenario-based multiple choice
40 questions set in situations a security leader actually faces.
Eight written leadership responses
Board memos, budget cases and incident summaries, graded by a senior practitioner on judgment and defensibility.
Pass mark 75%
Earns the CAISO practitioner-level certification.
The Shadow AI Reckoning
A discovery audit becomes an AI Tool Register and a 5-pillar Acceptable Use Policy, mapped to the EU AI Act and GDPR Art. 22.
The Ransomware Boardroom Game
Five roles, five stages, one $20M attack — you defend the pay-or-not-pay call under a hard deadline.
The Poisoned Matrix: AI Security War Room
A five-stage adversarial AI incident at NimbusMind, run from five executive seats through to governance reform.
- Architecture
SABSA, STRIDE at scale, PASTA
Enterprise security architecture and risk-centric threat modelling.
- Finance
FAIR model
Quantify risk in financial terms and build the security investment case.
- Regulation
EU AI Act, GDPR Art. 22, CISO personal liability
Regulatory engagement and where accountability actually lands, post-Uber.
- Measurement
NIST CSF Tiers, CMMI, C2M2, KPIs, KRIs
A 90-day CISO roadmap and the metrics to run it against.
- Advisory
Reviewed by practising CISOs and security leaders
The full roster, with roles and organisations, is listed at /course-advisors.
- Audience
Team leads, security managers and aspiring CISOs
Including those arriving from an adjacent function such as IT or risk.
CSA CCM v3.0.1 Addendum to the RBI Gopalakrishna Committee (GKC) Report
2018
Technology & Cloud Security Maturity Global Survey
2022, with CSA and OpenText
AI Empowering Cybersecurity
2024, with KDEM, VVCE, SDM IMD
Global Cybersecurity Skills Gap Report
2025, with KDEM, VVCE, SDM IMD
State of Agentic AI 2026
Ongoing research into how autonomous agents detect, reason and respond to security threats faster than humans.
How You’ll Be Certified
Learn
Attend all nine modules taught live across five evening sessions and the Saturday immersion. Six pair a leadership framework — SABSA, STRIDE/PASTA, maturity models, board communication, FAIR, KPIs/KRIs — with what changes once AI and personal liability are in the picture, and set an assignment to apply it. Three run as live boardroom crisis simulations: the Shadow AI audit, a $20M ransomware attack, and a five-stage adversarial AI incident.
5 evenings + immersion day
Live the Scenario
One continuous narrative tenure runs across all nine modules — the same CFO, CEO, General Counsel and mentor CISO recur and escalate, so a skill you build translating risk to the board in Module 4 is the one you are tested on live under fire in the crisis simulations.
One executive cast, nine modules
Assess
Sit the CAISO certification assessment: 40 scenario-based multiple-choice questions set in situations a security leader actually faces, plus 8 written leadership responses graded by a senior practitioner, not auto-scored.
40 MCQs · 8 written responses
Certify
Score 75% or above to earn the CAISO certification — a practitioner-level credential demonstrating executive-level security leadership capability, awarded on judgment a human reviewed.
Pass mark: 75%
Frameworks and standards this programme is built on
CAISO is a practitioner-level credential in its own right, not exam preparation. These are the frameworks the nine modules teach and apply directly — the same ones your board, your auditors and your regulator already use, so the vocabulary you leave with is theirs rather than ours.
| Body | Framework / standard | Why it matters |
|---|---|---|
| The SABSA Institute | SABSA Enterprise Security Architecture SABSA | The layered architecture model used in Module 1 to design security from business drivers down to implementation. |
| The Open Group / FAIR Institute | FAIR — Factor Analysis of Information Risk FAIR | The quantification model behind the budget module — how a risk becomes a number a board and a CFO will argue with. |
| NIST | NIST Cybersecurity Framework NIST CSF | One of three maturity models used to baseline a programme and structure the 90-day roadmap. |
| ISO/IEC | ISO/IEC 27001 ISO 27001 | The management-system standard your programme will be audited against, referenced throughout the programme and metrics modules. |
| Microsoft / VerSprite | STRIDE and PASTA threat modelling STRIDE / PASTA | Applied at enterprise scope in Module 2, including AI as both threat actor and threat-modelling tool. |
| European Union | EU AI Act | Risk classification for the Shadow AI Tool Register, and where CISO personal liability actually lands. |
SABSA Enterprise Security Architecture
The layered architecture model used in Module 1 to design security from business drivers down to implementation.
FAIR — Factor Analysis of Information Risk
The quantification model behind the budget module — how a risk becomes a number a board and a CFO will argue with.
NIST Cybersecurity Framework
One of three maturity models used to baseline a programme and structure the 90-day roadmap.
ISO/IEC 27001
The management-system standard your programme will be audited against, referenced throughout the programme and metrics modules.
STRIDE and PASTA threat modelling
Applied at enterprise scope in Module 2, including AI as both threat actor and threat-modelling tool.
EU AI Act
Risk classification for the Shadow AI Tool Register, and where CISO personal liability actually lands.
Framework and standard names are the property of their respective owners and are used here only to identify what this curriculum teaches. CyBe Global is not affiliated with, endorsed by or accredited by any of these bodies, and this programme is not an official preparation course for any of their certifications.
Faculty for This Course
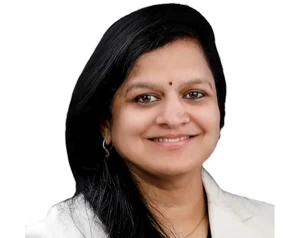
Satyavathi Divadari
Founder and CEO · CyBe Global · Founder, CSA Bangalore Chapter
Satyavathi Divadari
Founder and CEO · CyBe Global · Founder, CSA Bangalore Chapter
28 years on the hiring side of enterprise security, CISSP, US patent holder
Satyavathi Divadari spent twenty-eight years as the buyer before becoming the builder. Across security roles at Wells Fargo, Cognizant, Capgemini and IBM, holding a CISSP and a US patent, she spent those years deciding who to hire into security-leadership roles, which skills actually mattered in that room, and which training was worth trusting.
She also founded the CSA Bangalore Chapter and built it into a community that has won the Cloud Security Alliance’s global Chapter of Excellence award three years running — the same practitioner network that reviews CAISO’s curriculum today.
Why this facilitator, for this course
CAISO teaches the boardroom: defending a budget to a CFO, translating risk for a CEO, knowing where personal liability lands. Satyavathi has sat on the other side of that exact table — as the enterprise security leader deciding budgets and evaluating who was ready for the CISO seat — for twenty-eight years across four global employers. She is not teaching the boardroom from a textbook; she is teaching the room she worked in.
Course Advisors
Practising security leaders who review this curriculum and keep it current.
R S Lakshminarayanan
GM & Regional CISO · Wipro Limited
Shobha Jagathpal
Managing Director · Morgan Stanley
Ashish Shrivastava
Director – Cyber Security · Honeywell
Ravi Subbiah
Managing Partner · TCS Ltd
What Learners Say
“This was different learning experience all together. So much fun and so much to learn. The energy was continuously high to know what’s next. Not just regular content but every time something new and different. I recommend this learning methodology to every learner.”
Pravinkumar Jha
Head of Product and Cloud Security
“That sounds like such a refreshing change from usual conferences. Learning through music and teamwork really makes complex concepts stick in a fun way.”
Rohan Pinto
CTO and Founder, 1Kosmos